What happens to your operating data.
This page describes the state of things, not the intention. What is established stands here with its reason. What is still open stands below as an open point — not as a promise nobody could redeem.
Where the data comes from and where it goes
Four stations. At each one it says what happens there and what does not.
- 01
Your till
The data arises in your till system. The recording duty stays there.
- 02
Veydex Connect
Connect brings it into the Hub. We do not ask for your till password.
- 03
Veydex Hub
In the Hub it sits separated per workspace: one workspace, one business.
- 04
Modules and helpers
Only booked modules compute on it. A helper sees only the data of its remit.
The four stations in detail
- Your till
- The data arises where sales happen — in the till system already at your place. Veydex changes nothing about that: if you link it over Connect, the recording duty under TSE, GoBD and Kassensicherung stays with your till system.
- Veydex Connect
- Connect brings it into the Hub — over one of five routes: an API, a cloud connection, a local connection, a direct integration or the legally mandated till export. We do not ask for your till password; where you grant access in your provider's account, you can revoke it there. If you would rather sign in with your till login inside the Hub, you can: the credentials pass once through our server to the provider, and only the access created there is stored, not the password.
- Veydex Hub
- In the Hub it sits separated per workspace. A workspace is one business: own settings, own team, own modules. Anyone running several businesses has one login and still separate sets of data.
- Modules and helpers
- What computes on it computes only on what has been booked. A module you have not booked processes nothing, and a helper sees only the data of its remit.
Who in the business may see what
At Veydex, authorisation is not a setting applied afterwards but part of every access.
Data separated per workspace
Five roles
Owner, shift lead, accounting, view only and staff, assigned per workspace.
Checked on every access
Not only at sign-in: a withdrawn role takes effect in an open session too.
Separated per workspace
Access to one workspace is not access to the others.
Analysis without personal reference
Staff-related analysis is aggregated by default.
Details
- Five roles
- Owner, shift lead, accounting, view only and staff. The role applies per workspace, not per login — whoever runs one site and helps out at another has the right role at both. Accounting and view only change nothing. Changes take effect immediately.
- Checked on every access
- Authorisation is checked on every access, not only at sign-in. A withdrawn role therefore takes effect in an open session too.
- Separated per workspace
- The data of several businesses sits separately. Access to one workspace is not access to the others.
- Analysis without personal reference
- Staff-related analysis is aggregated by default. “Shrinkage & voids” works without personal reference; it can only be switched on under defined conditions — so that hard-working staff do not automatically look like a problem.
What a helper may do — and what it may not
Observing and proposing is not the same as executing — and Veydex does not treat it as if it were.
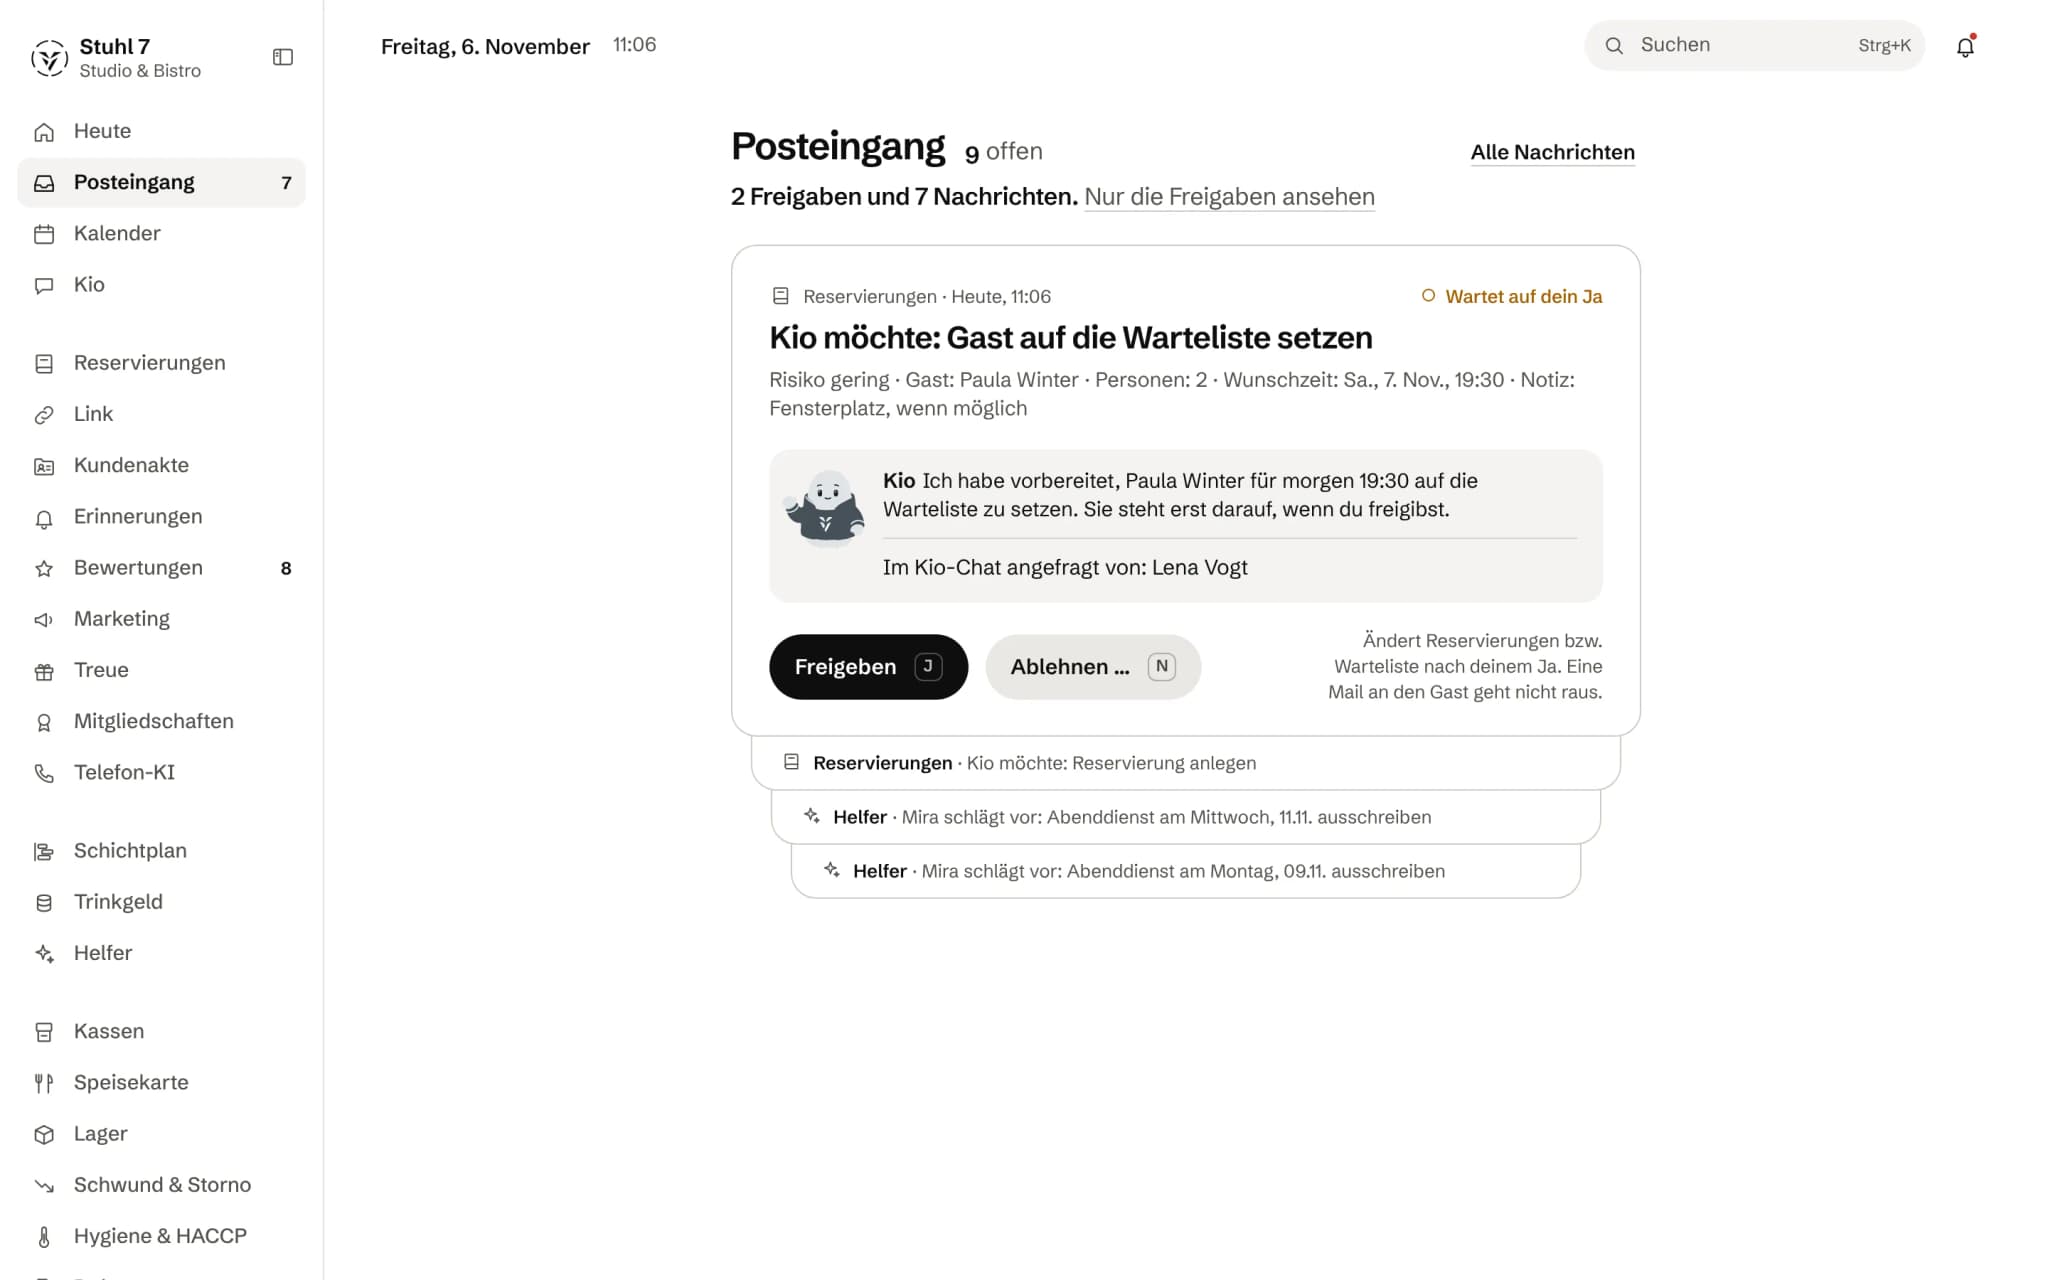
- 1Observe
- 2Propose
- 3ExecuteNone starts at this level.
How an approval runs
Proposal
A helper or Kio puts forward what should happen.
Your yes
Critical actions can require your confirmation.
Approve or decline
If you object, it does not happen.
In the history
What a helper has done stays traceable.
Three levels
Observe, propose, execute. You set which one applies per helper.
Clear limits before anything runs
Every automated action follows defined permissions and safety limits.
Objection beats proposal
If you object, it does not happen.
Only its own data
Every role sees only the data of its remit.
Traceable and switchable
What a helper has done stays in the history. Switching off works at any time.
Details
- Three levels
- Observe, propose, execute. You set which one applies per helper. None starts at the highest level.
- Clear limits before anything runs
- Every automated action follows defined permissions and safety limits. Critical actions can require your confirmation on top.
- Objection beats proposal
- If you object, it does not happen. And Veydex never widens on its own what a helper may do.
- Only its own data
- Every role sees only the data of its remit. Ben sees purchasing and stock, not the guest profiles.
- Traceable and switchable
- What a helper has done stays traceable in the history. The helpers can be switched off at any time — all of them, or one at a time.
Getting it out and deleting it
- While runningCSV from Analytics and several modules
- After the contract endsExport stays possible for a period
- After thatReturned or deleted, as you choose
Export while running
CSV from Analytics and from several modules, no DATEV posting batch.
Export after the contract ends
After that the data is returned or deleted, as you choose.
Statutory retention
Where the law requires retention, processing is restricted instead of deleted.
Applications
A dedicated storage area, deleted 180 days after arrival.
Details
- Export while running
- Analytics gives a CSV export, and several modules export their own data — guest records, hygiene, shrinkage & voids. That is a sheet of numbers, not a bookkeeping file; the Hub does not produce a DATEV posting batch.
- Export after the contract ends
- After the contract ends, an export remains possible for 30 days. After that the data is returned or deleted, as you choose.
- Statutory retention
- Where a statutory retention duty applies, processing is restricted for its duration instead of the data being deleted. That is not an exception in Veydex's favour but what the law requires.
- Applications
- Documents from the job application form sit in a dedicated storage area at Hetzner, separated from everything else, and are deleted automatically 180 days after they arrive. What is promised is deletion at the latest six months after the procedure ends.
What this website itself does
The rest of this page is about the Hub. This section is about the page you are on — and it is deliberately built narrow.
No consent banner, because nothing is stored
Reach measurement without cookies, on a self-hosted Umami instance.
Fonts are served locally
No transmission of your IP address to a third-party font server.
No captcha
We catch automated requests without analysing visitors.
Appointments over Cal.com
Used only for appointments on this website, not in the Hub.
Details
- No consent banner, because nothing is stored
- Reach measurement runs on a self-hosted Umami instance without cookies. The origin of a visit — campaign, referrer — lives only in the tab's memory and not on your device. That is why the site needs no banner.
- Fonts are served locally
- No fonts from a third-party server, so no transmission of your IP address to one.
- No captcha
- We catch automated requests without bringing in a service that analyses visitors.
- Appointments over Cal.com
- Appointment booking runs over Cal.com. What is transmitted stands in the privacy policy — the service is used only for appointments on this website and not in the Hub.
Operation
- Operation and server location
- Hetzner Online GmbH, Industriestr. 25, 91710 Gunzenhausen, Germany, with data centres in Germany and Finland, i.e. within the EU
- Storage for applications
- Hetzner Online GmbH, in data centres within the EU
- Sending messages
- Brevo SAS, 106 boulevard Haussmann, 75008 Paris, France, with data centres in the EU. Messages arrive in our mailbox at Zoho Corporation B.V., Beneluxlaan 4B, 3527 HT Utrecht, Netherlands, also with data centres in the EU
- Competent data protection authority
- Unabhängiges Landeszentrum für Datenschutz Schleswig-Holstein (ULD), Holstenstraße 98, 24103 Kiel
Data processing
If you use the Hub, Veydex processes personal data on your behalf — guests, staff, transactions. There is a data processing agreement for that, with annexes on technical measures and sub-processors. It exists as a draft and should be requested before signing; legal review is still outstanding, and the document says so itself.
What is not answered here yet
These details do not yet exist internally in a form we could commit to publicly. They stand here rather than being absent — anyone who needs them for a decision gets them in conversation, and they come onto this page once they are settled.
- Encryption methods for stored data, named individually
- Backups and recovery: frequency, retention, tested target times
- A committed availability. The status page shows the current state; that is not a commitment.
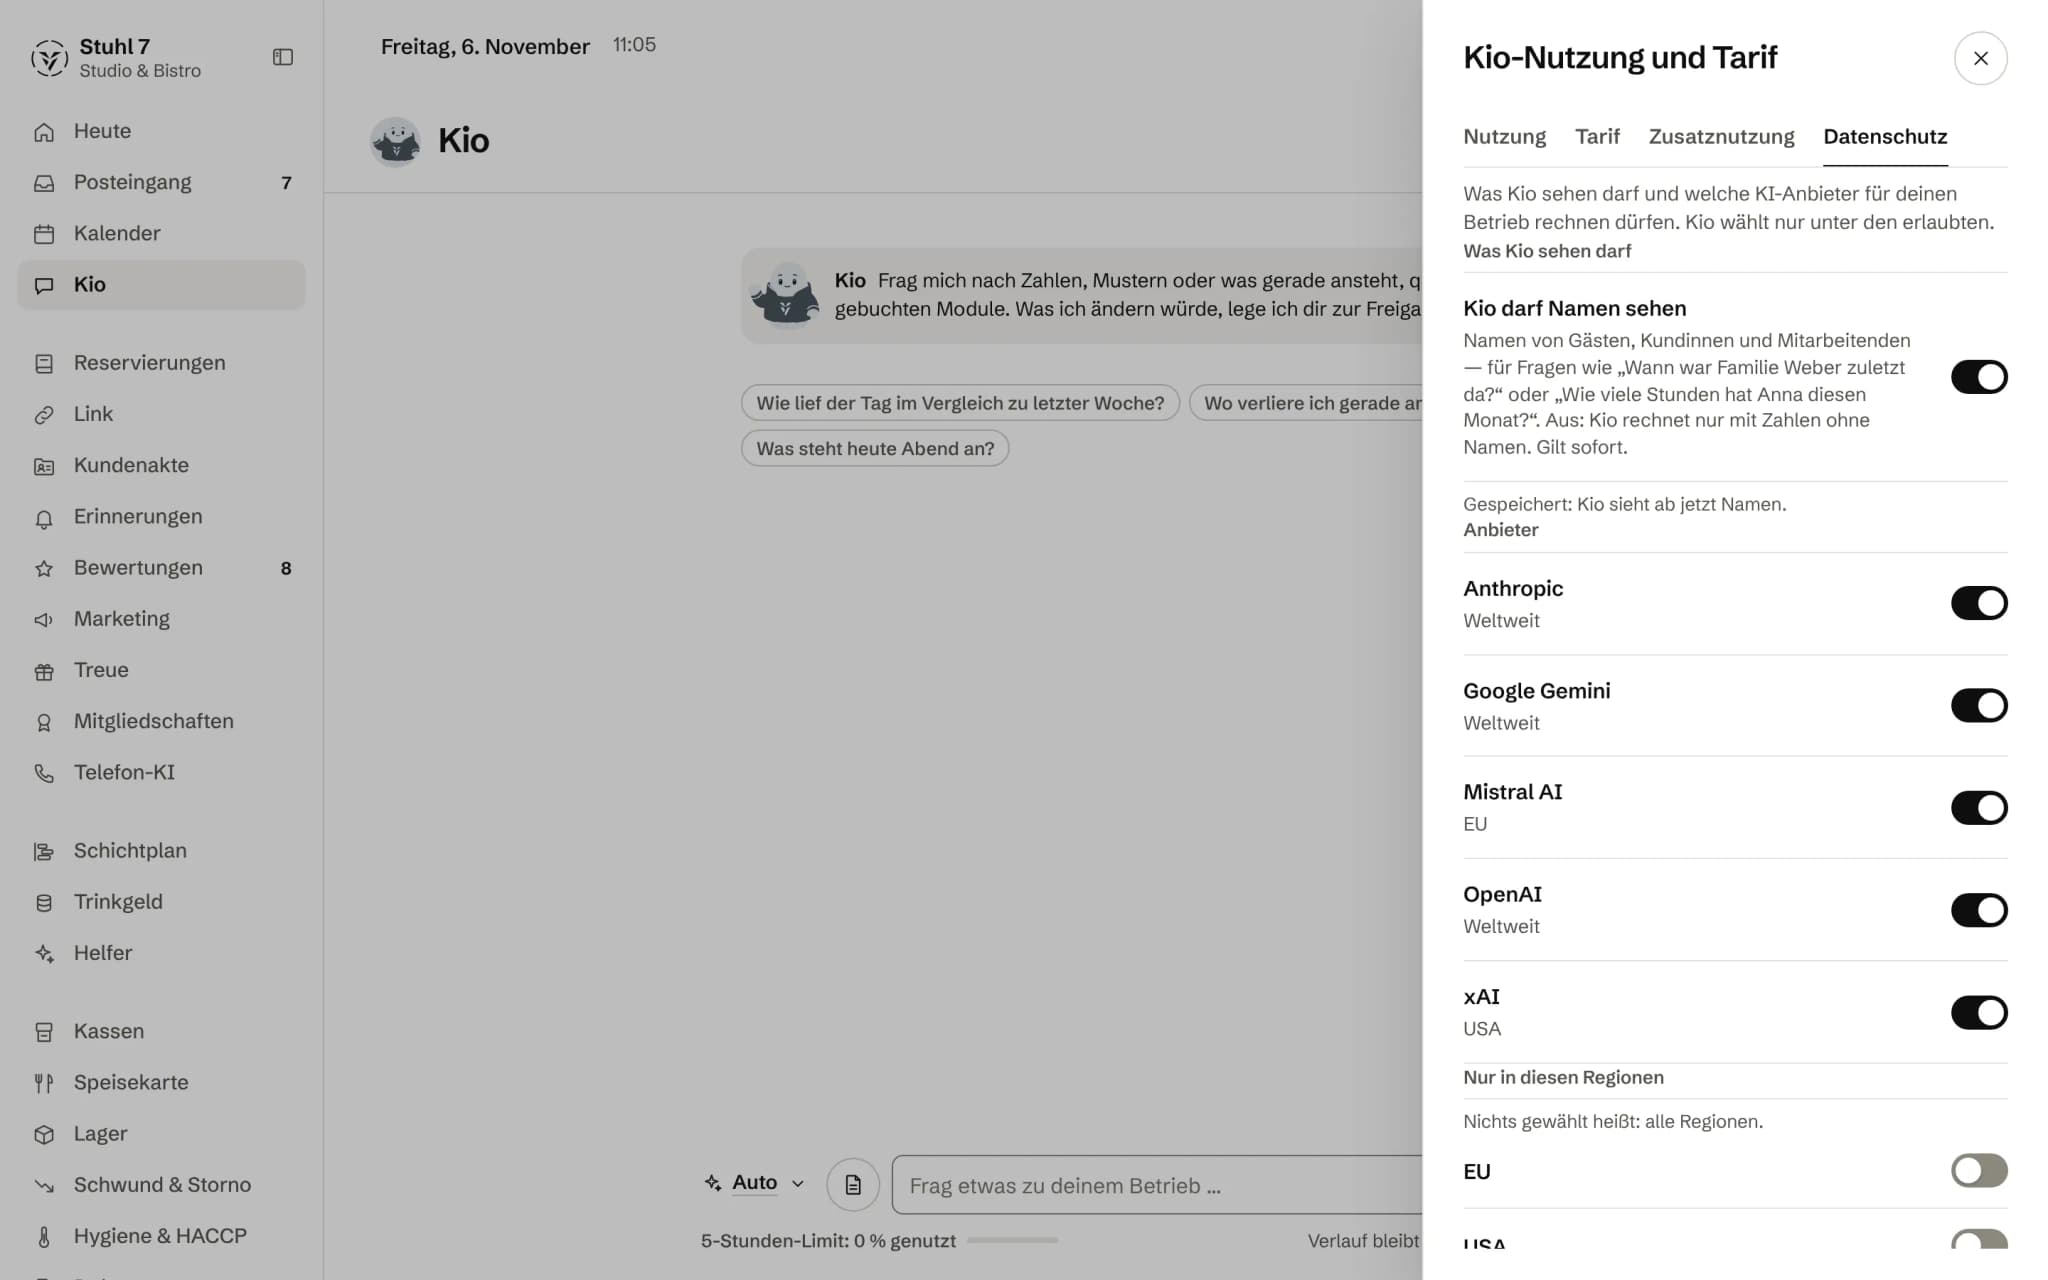
- Which AI providers stand behind phone AI and the helpers, and where they process
- Reporting route and deadlines for a security incident, stated publicly
- Certifications and audit reports — none exist, and this page claims none
Questions that are not answered here?
If you need a detail for a decision that this page leaves open, ask for it. An honest answer in conversation is worth more than a sentence on a page that nobody can back up.